Security engineer · Singapore
Security engineer who builds.
I do security risk and compliance for a living. Outside work I build things people actually use, run my own servers, keep AI on a short leash, and chase bugs down to the real cause.
the two big onesSelected work
Each opens a short case study: what it is, the calls I made, and what I got wrong.
-
Product suite, solo
Versed
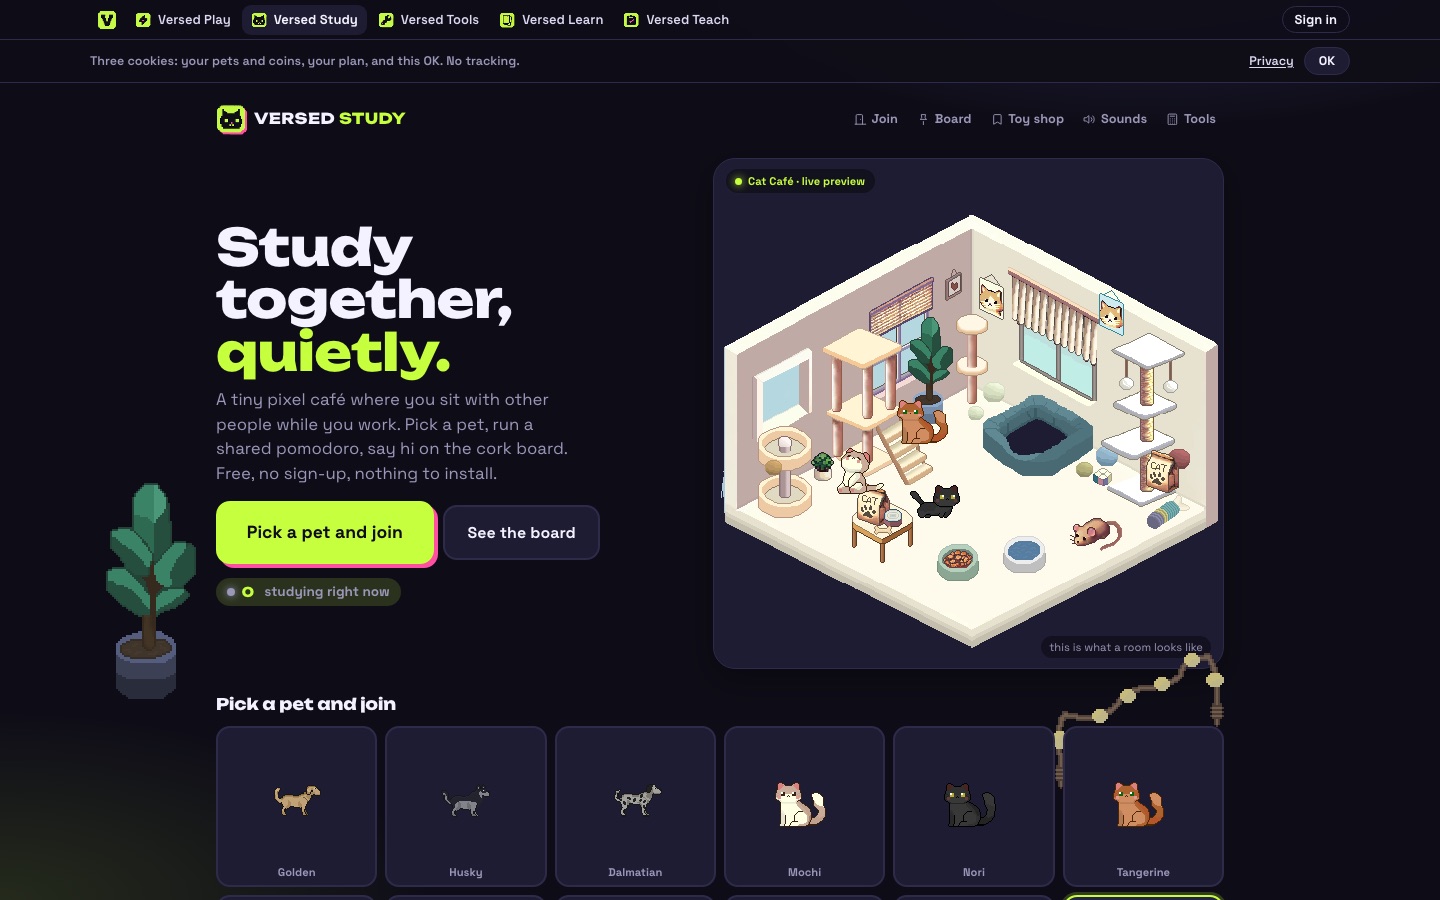
Four free learning tools for students, tutors and teachers. I designed, coded and run all of it.
- 4 products live
- no sign-up, no tracking
- 1 person: design, code, ops
-
Blue team, Python
Detection tooling
A log triage pipeline, a phishing link checker and tested Sigma rules, all public with passing builds.
- 10 Sigma rules across 15 ATT&CK techniques, green in CI
- 12 public repositories with passing builds
useful, but supervisedAI engineering
I use AI every day, and I don't trust it by default. Everything here has a limit, a test or a person checking the model's work, because that's the bit most AI projects skip.
Play "Break my bot" a six-level game I made. Try to talk a chatbot into leaking its password and see which defences hold up.
-
Versed
AI inside a free product for kids
An AI helper in Versed Study with a hard cap on it, and AI-built flashcard decks in Versed Learn. Both are in tools students use.
The guardrailLimits per visitor and per day live in a Durable Object, after I proved a KV counter can't hold a rate limit. A deck costs about 3 cents to generate, so the free tier has a real number behind it. No user photo uploads on public content, and chat goes through a word filter with reporting.
Write-up: the rate limit that did not limit -
DART assignment, 2025
AI marking for a selection exam
I rebuilt an early prototype into an AI marking system for a cybersecurity bootcamp's selection exam: Claude on AWS Bedrock, versioned prompts and an evaluation harness. It marked several hundred scripts, past papers and live applicants.
The guardrailI didn't trust anything I hadn't measured. Every prompt change got re-run against the instructors' marking, and agreement went from about 60% to about 77%. That number is the point. The model is a fast first marker, not the judge, and the disagreements are where a person needs to look.
On my CV -
GitHub, open source
Open-source tools for AI security
Three small tools that came out of my own AI work: regression tests for prompt-injection defences, a bit-level check of a model file against the base it claims, and a probe that tells you if a model really calls tools.
The guardrailAll three grade on facts, not opinions. A random token either came back or it didn't. A bit either changed or it didn't. None of them needs a second model to judge the first, and each README says what it can't do, including the case the model audit can't see.
Code and passing tests on GitHub
three kinds of workWhat I'm good at
The work I do most, and the tools I usually reach for in each.
Detection and response
I do log analysis, SIEM work and incident handling. I write detections other people can read and test, and I keep digging until I can name the one thing that caused it.
Security-minded infrastructure
I run Linux, containers, networking and monitoring as code, with backups I've actually restored from and a threat model I can explain.
Shipping secure products
I take products from a blank page to real users on Cloudflare's edge, and I sort out privacy and abuse as part of the design, not as a patch later.
the side projectsMore work
Stuff I run on my own hardware, plus the small open-source tools that fell out of it.
-
Performance engineering
Local AI on 2017 hardware
A 35-billion-parameter model made 44% faster on nine-year-old GPUs by measuring every assumption.
- 46 to 71 tokens a second
- +44% on the same hardware
- 1 crash found before it shipped
-
Infrastructure, self-hosted
One box, forty services
A recycled gaming PC running my family's photos, passwords, media and AI, reachable from anywhere and exposed to no one.
- 40+ services
- 0 ports open to the internet
- 14 days of restorable backups
Also built
- pdf-redaction-checkChecks whether redacted text in a PDF is really gone. It finds words still under black boxes, overlays included, and redaction marks nobody applied. Rewritten after a real document got past my first version.
- llm-guardrail-testsRegression tests for the guardrails on your own AI feature: 20 known prompt-injection patterns, graded deterministically with random markers and a canary instead of a judge model. Drops into CI.
- model-diff-auditCompares an AI model bit by bit against the base it claims to come from, and tells normal fine-tuning apart from tampering. On a real tampered model, it found the 90 edited rows out of 151,936.
- toolcall-probeAsks a local model endpoint straight out whether it really calls tools or just talks about calling them, and tells you which layer is to blame.
- cctokensShows where your Claude Code tokens go: usage and API-equivalent cost by day, model and project. One Python file, no dependencies, nothing leaves your machine. Counts each message once, unlike the logs.
- docker-gpu-reload-checkFinds containers that will quietly lose their NVIDIA GPU on the next systemd reload, and prints the fix. Read-only. Tested on my own two-GPU server.
- private-relay-blockGets Apple devices back behind the network's DNS filter by blocking iCloud Private Relay the way Apple documents it, plus the cached relay addresses. Has a dry run and a clean undo.
- disc-image-idTells Xbox, PS1 and PS2 disc images apart by their signature instead of the file extension, and converts the full Xbox dumps the xemu emulator refuses. Tested and open source.
- Exam-practice tutoring appA primary school English app for students and teachers, built with a partner who owns the backend. Hints fade as a student gets the hang of it, and teachers see every attempt. Still in development.
what it looked like, then what it wasRoot-cause write-ups
Real things that broke on systems I run, and what was actually behind each one.
what they saidwhat it was
- A per-minute request cap let through several times the cap. KV reads are cached for a minute. A stale counter cannot enforce a window. SOLVED
- Ad blocking stopped on one phone. The filter logged nothing. iCloud Private Relay resolves names through Apple, so the filter was never asked. SOLVED
- One TV channel played everywhere except my media server. ffmpeg 7.1 refuses video segments whose URL has no file extension. SOLVED
- Three GPU services died at the same minute and nothing logged an error. A systemd reload wiped device rules Docker never knew about. SOLVED
- The emulator rejected every disc image I dumped. Full dumps put the game partition at 0x18310000. The emulator reads 0x10000. SOLVED
- Game streams worked but looked soft and lagged. The encoder was built without this GPU's kernels and silently fell back to the CPU. SOLVED
- The agent says it will search the web, then does nothing. A hidden text-only tool mode, plus tool definitions silently cut off by a context mismatch. SOLVED
- A 35B model ran at 46 tokens a second. Was that the hardware? No. Runtime and four defaults. 71 tokens a second on the same cards. SOLVED
About
I work in cybersecurity full time, on the risk and compliance side. I also tutor special needs kids, and have since 2020. That's why the Versed tools exist and why they're free: my students needed calmer, simpler tools than the ones schools pay for, so I built them.
Most of my training has been hands-on. I hold the GIAC Certified Incident Handler and worked through Hack The Box's SOC analyst path. My favourite part of any investigation is when a vague "it's broken" turns into one specific line in one specific log.
Six years of teaching kids who struggle with reading has made me good at something most engineers dodge: explaining a hard thing to someone who isn't technical, without talking down to them.
Credentials
- BSc (Hons) Computer Science, First Class HonoursCoventry University, United Kingdom
- Diploma in Information TechnologyPSB Academy, Singapore
- GIAC Certified Incident Handler (GCIH)SANS SEC504: Hacker Tools, Techniques and Incident Handling
- Hack The Box AcademySOC Analyst path: SIEM, Windows event logs, incident handling
- Red AlphaCybersecurity specialist training, Singapore
- CSIT TISC CTFNational capture-the-flag. In 2026, the year AI tools were allowed, cleared four of ten levels in a single day.
Get in touch
I read and reply to every message. Happy to walk through any of this on a call, too.